Supabase
Connect Supabase as an access review source using a personal access token so Probo can list the members of your Supabase organization.
Probo reads your Supabase organization’s members through the Supabase Management API so you can review who has access.
Prerequisites
Section titled “Prerequisites”- Probo organization administrator access
- A Supabase account with an organization role in the organization you want to review. Every organization role (Owner, Administrator, Developer and Read-Only) can list organization members. An account with access to specific projects only cannot select the organization for an Organization token. A token never has more access than the account that created it
- The Organization Slug of the organization Probo should review, which the connect form asks for alongside the token. Supabase puts it in the dashboard URL while the organization is open:
supabase.com/dashboard/org/<organization-slug>
Collected Fields
Section titled “Collected Fields”| Probo field | Supabase field | Notes |
|---|---|---|
| Name | user_name | The member’s Supabase user name. There is no fallback, so a member returned without one is listed with an empty name |
email | ||
| Role | role_name | The members endpoint returns one role name per member. Supabase’s organization roles are Owner, Administrator, Developer and Read-Only. Probo trims surrounding whitespace, and a member returned without a role name is listed without one |
| Admin | role_name | Flagged as an administrator when role_name is Owner or Administrator, and not for Developer or Read-Only |
| Status | Not supported | |
| MFA | mfa_enabled | Enabled when the flag is true, disabled otherwise. Supabase returns the flag for every member |
| Last login | Not supported | |
| External ID | user_id | Stable identifier used to track the account across reviews |
| Created at | Not supported |
Step 1: Create a Personal Access Token
Section titled “Step 1: Create a Personal Access Token”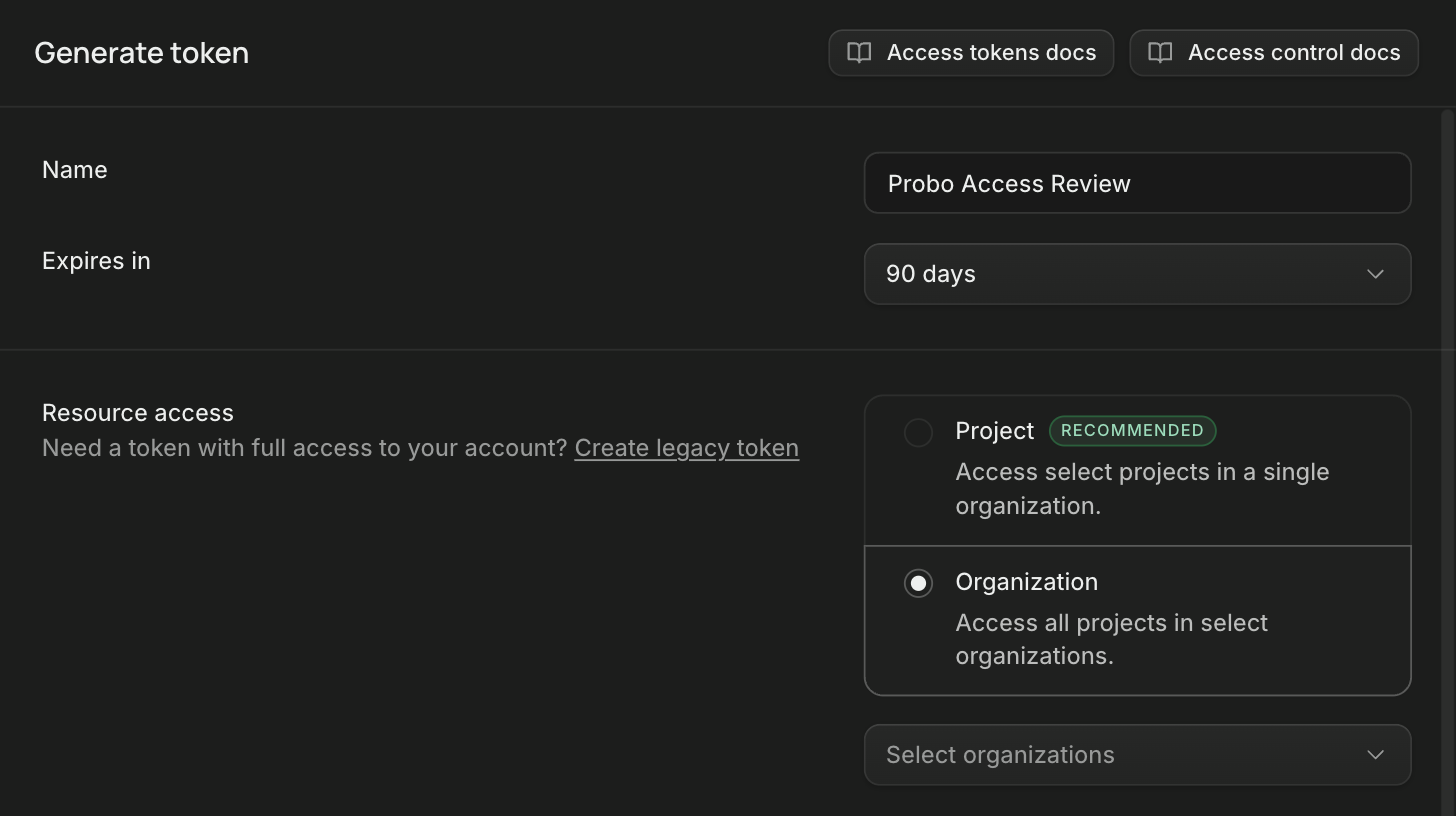
- In the Supabase dashboard, go to Account Settings > Access Tokens and click Generate new token.
- Enter a Name (e.g.
Probo Access Review) and set Expires in. The dialog defaults to 7 days, so pick 90 days or a Custom date that covers your review cycle. - Under Resource access, select Organization instead of the default Project, then choose the organization Probo should review in Select organizations.
- Under Permissions, open Account and organization and set Organization Members to Read. Probo reads nothing else, so leave the other permissions at None.
- Click Review access, then Create token. Copy the token (
sbp_…) and store it securely. Supabase shows it once and you cannot retrieve it afterwards.
Step 2: Connect in Probo
Section titled “Step 2: Connect in Probo”- In Probo, go to Settings > Connectors and click Add more to open the Marketplace.
- Find Supabase and open it.
- Enter a Name for the connection (e.g.
main), paste the token into API key, enter your Organization Slug, and click Connect. - Go to Access Review > Sources, click Add sources, tick Supabase, and click Add.
When you click Connect, Probo uses the token to request that organization’s members from Supabase. If Supabase has no organization with that slug, or accepts the token but refuses to list that organization’s members, Probo shows a Could not connect error with the reason and does not save the connection. After you add the source, Probo names it after your organization slug and pulls its members into your campaigns.
Troubleshooting
Section titled “Troubleshooting”- Token rejected. The connect form only accepts a key that starts with
sbp_, so a project API key is refused before it reaches Supabase. An expired or deleted personal access token is not caught when you connect: the source then shows Supabase credentials are invalid. Confirm the token is still listed under Account Settings > Access Tokens. - “This access token cannot read the members of this organization.” Shown in the Could not connect error when you click Connect. The token has the default Project resource access, is scoped to other organizations, or belongs to an account that is not a member of this organization. Generate a token with Organization resource access that includes the organization and Organization Members set to Read.
- “Supabase has no organization with this slug.” Open the organization in the Supabase dashboard and copy the Organization Slug from the URL:
supabase.com/dashboard/org/<organization-slug>. - Syncs worked and then stopped. The token has expired, or the account that created it has left the organization. A token has only its owner’s access, so it stops reading the organization once that person leaves. Generate a new token, then click Update API key (the key icon) on the Supabase connector in Settings > Connectors, paste the new token, and click Save API key. The connector keeps its name and its source, so existing campaigns keep fetching it.
- Using a legacy token. A legacy token has full access to your account and shows a LEGACY badge on the Access Tokens page. Tokens created before Supabase introduced scoped tokens are legacy tokens, and so are tokens made with Create legacy token. A legacy token works, but it grants far more access than Probo needs. Prefer a token scoped as described in Step 1.